
A few years ago, “AI-powered security” was mostly a marketing phrase stapled onto products that hadn’t changed much underneath. That’s not really true anymore.
Attack volume has grown past what human analysts can triage manually, and the attacks themselves have gotten faster and more automated too — some of them AI-driven on the offensive side. Defending against that with static rules and manual review doesn’t hold up the way it used to. AI-driven cybersecurity software isn’t really an upgrade at this point. It’s closer to a baseline requirement for anyone handling real volume or real risk.
This piece looks at what these systems actually do, the components that make up a real deployment, and what to weigh before adopting one.

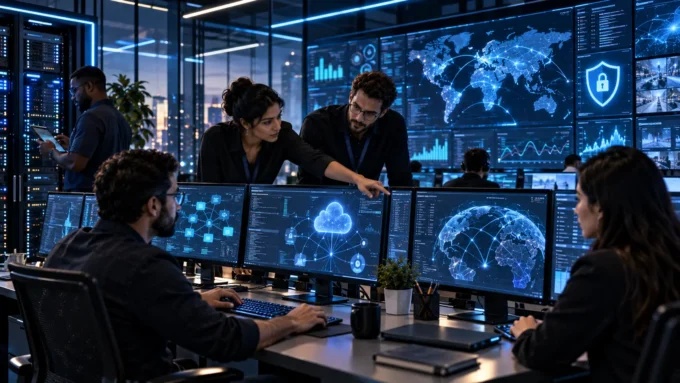
Modern security operations centers increasingly rely on AI to surface the handful of alerts that actually matter out of thousands generated daily.
Why Traditional Security Tools Are Struggling to Keep Up
Signature-based detection — the older model of flagging known malware by matching it against a database — was built for a world where threats repeated themselves often enough to catalog. That world doesn’t really exist anymore. New attack variants get generated faster than any signature database can keep pace with, and a lot of modern intrusions don’t look like malware at all; they look like a legitimate user doing something slightly unusual.
That’s the specific gap AI-driven tools are built to close. Instead of asking “does this match a known threat,” the software asks “does this behavior deviate from what’s normal here,” which catches things a rules-based system was never going to flag in the first place.
Core Capabilities of AI-Driven Cybersecurity Software
1. Behavioral Anomaly Detection
Rather than relying purely on known threat signatures, machine learning models build a baseline of normal activity for users, devices, and network traffic, then flag deviations. A login at 3 a.m. from an unfamiliar location, or a sudden spike in data transfer from an account that’s never done that before, gets surfaced automatically instead of buried in a log file nobody’s watching in real time.
2. Automated Threat Detection and Triage
Security teams get flooded with alerts, and most of them are noise. AI models trained on historical incident data can prioritize which alerts actually warrant human attention, cutting through the volume so analysts spend their time on real threats instead of chasing false positives all day.
3. Phishing and Social Engineering Detection
Natural language processing models can flag phishing attempts by analyzing email content, sender behavior patterns, and structural anomalies that a human skimming an inbox might miss. This matters more every year as phishing attempts themselves get more convincing, sometimes generated by AI on the attacker’s side too.
Phishing remains one of the most common entry points for breaches, which is why detection has become one of the most heavily invested areas in AI security tooling.
4. Endpoint Detection and Response (EDR)
Modern endpoint protection goes beyond antivirus scanning, using behavioral models to catch fileless malware, unusual process activity, and privilege escalation attempts happening in real time on individual devices, then automatically isolating a compromised endpoint before it can spread further.
5. Fraud Detection and Risk Scoring
For platforms handling transactions, AI models score risk in real time based on behavior patterns, device fingerprints, and transaction anomalies, catching fraudulent activity that would slip past simple rule-based thresholds.
6. Automated Incident Response
Some platforms go a step further than detection, automatically taking containment actions — isolating a device, revoking a session, blocking a suspicious IP — the moment a high-confidence threat is identified, cutting the response window from hours down to seconds.
7. Vulnerability Management and Predictive Risk Scoring
AI models can prioritize which vulnerabilities in a system are actually likely to be exploited based on real-world attack patterns, rather than treating every flagged issue as equally urgent. This helps security teams fix what matters most first instead of working through an undifferentiated backlog.
8. Network Traffic Analysis
Continuous analysis of network traffic patterns can catch lateral movement inside a network — the stage of an attack where someone who’s already gotten in starts moving toward more valuable systems — often before real damage is done.
9. Compliance Monitoring and Reporting
Automated systems can continuously check configurations and access patterns against regulatory requirements, flagging drift before it becomes an audit finding instead of after.
10. Threat Intelligence Integration
The strongest platforms pull in external threat intelligence feeds and correlate them against internal activity, catching emerging attack patterns that haven’t shown up in an organization’s own environment yet but are already circulating elsewhere.
What to Weigh Before Adopting AI-Driven Security Tools
AI models are only as good as the data they’re trained on, and a system dropped into a new environment usually needs a tuning period before it stops generating too many false positives or missing context-specific normal behavior. It’s also worth being clear-eyed that AI-driven tools augment a security team rather than replace it — the judgment calls around ambiguous incidents still need a human in the loop, at least for now.
The organizations that get the most value tend to treat this as an ongoing partnership with their tooling rather than a one-time install, feeding back incident outcomes so the models keep improving over time.
Why Choose Web Squalix
Building or integrating AI-driven cybersecurity software isn’t something to hand to a generalist team. Web Squalix approaches security-focused development the way the category demands — with threat modeling, data architecture, and compliance treated as first-order design decisions rather than something patched in after a prototype is already built.
The team’s experience spans multiple regulated and high-stakes industries, which means the pattern recognition brought to a security build comes from more than one context — not just a single narrow use case resold under a new name. Whether the need is anomaly detection tuned to a specific platform’s behavior, automated incident response workflows, or integrating existing threat intelligence feeds into a live system, the approach stays the same: architecture built around the actual threat surface, not a generic security checklist.
Security work doesn’t end at deployment either. Ongoing monitoring, model tuning, and updates as new attack patterns emerge are part of the engagement, because a security system that stops adapting starts falling behind the threats it was built to catch.
The tools available for defending systems have gotten genuinely powerful. The harder part is choosing who builds and tunes them around your actual risk — and that’s the decision worth spending real time on.
learn more :https://www.squalix.com